In six months of 2026 more breaches have already been notified than in the whole of 2025. Incidents at suppliers that drag in many customers, hotel booking software and ransomware weigh heavily.
They were weak keys in certificates trusted by browsers and systems. Browsers have already removed them; software that validates certificates on its own needs updating.
CISA asks organisations to apply patch BT26-05-RS on their own systems, limit their exposure and, if compromise is suspected, rebuild and rotate every stored credential. The cloud version is already patched.
INCIBE-CERT summarises the international operation: three arrests, five servers and the leak site seized, and at least 110 terabytes of stolen data secured.
14 October 2026 We all live, work and sleep inside a building, and we almost never think about who made sure it was built properly. Behind every building there is someone who turns the project into re...
OCU survey with other European associations (1,000 respondents in Spain): we repair little because accessible workshops and spare parts are lacking. A parallel study with BEUC concludes that ecodesign is already improving phone repair.
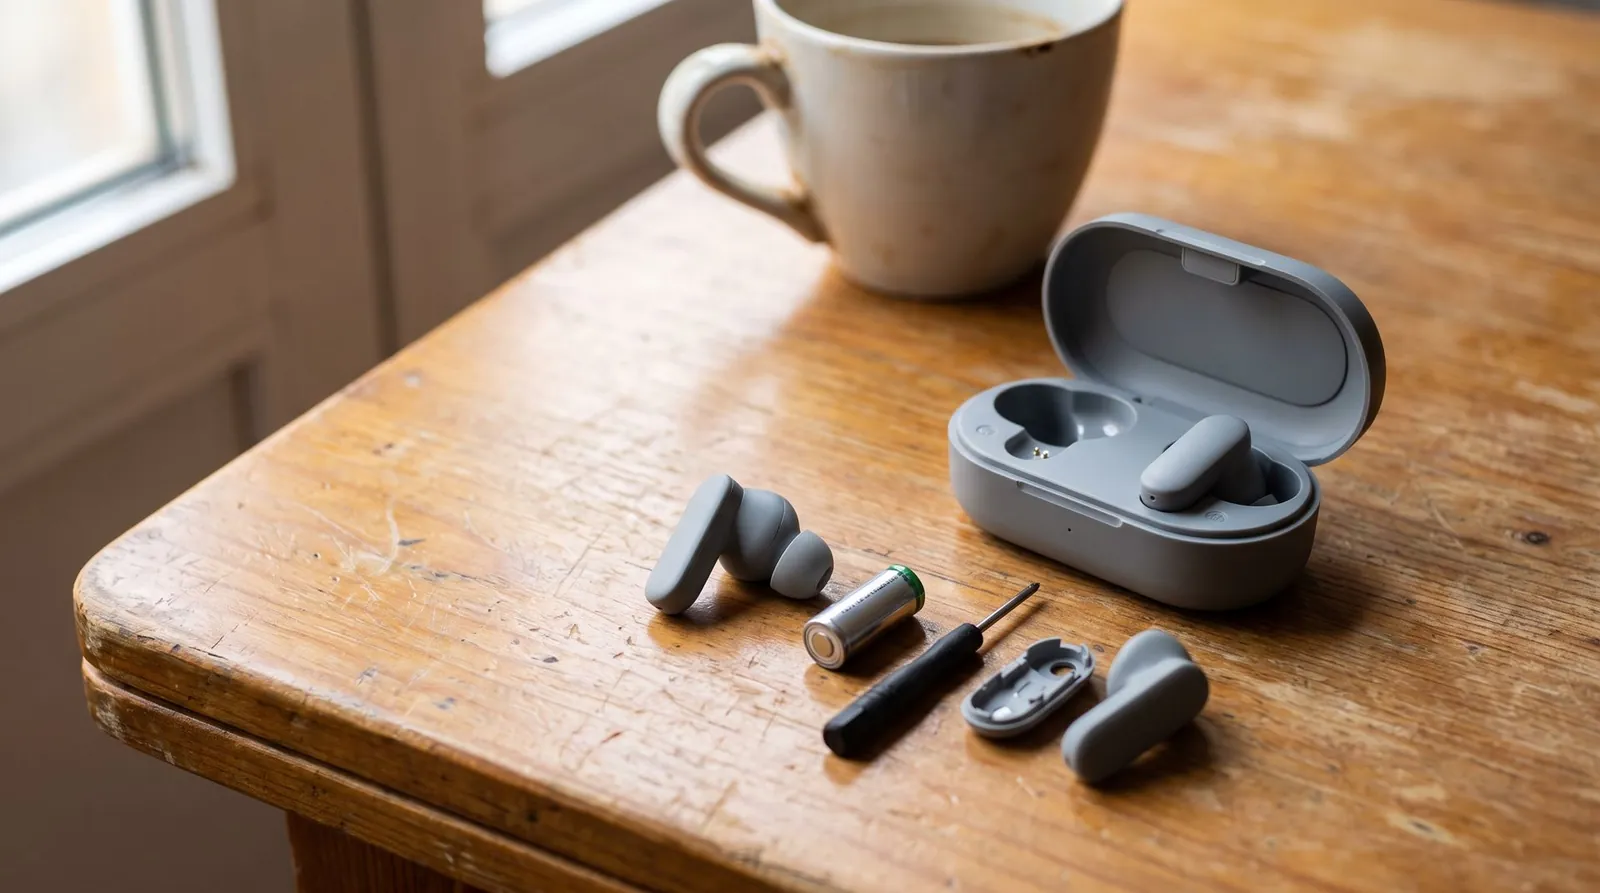
Fairphone launches wireless earbuds whose batteries and case the user can replace themselves. The "up to three years" warranty and future updates are the manufacturer's promises, with no specific deadlines.
CISA added it on 13 October to its catalogue of exploited vulnerabilities: update now and, if compromise is suspected, factory reset and change all credentials.
Ryan Dahl, creator of Node.js and Deno, joins Cloudflare with his team; they will merge celld and workerd so that self-hosting Workers becomes a first-class supported option.
The Anthropic Cyber Mission kicks off with a programme for industrial security providers with eleven partners and OSS Scanner, a free, voluntary service of bug reports generated by its models.
The new version of the Usage Policy takes effect on 12 November 2026 and spells out requirements for high-risk uses, autonomous hardware control, surveillance and unsupported regions.
Joint advisory AA26-281A describes how actors linked to the Chinese Government combine mass scanning, botnets and email theft on Exchange and Microsoft 365. It includes indicators and the exploited CVEs.